semanage
On RHEL, Rocky and Alma: changes the SELinux configuration permanently: file labels, allowed ports, booleans and permissive domains.
Syntax
semanage fcontext | port | boolean | permissive -l | -a | -d | -m [OPTIONS]
Options
| Option | Description |
|---|---|
fcontext -a -t TYPE 'PATH(/.*)?' |
Rule for which label files below a path get |
fcontext -l [-C] |
List the rules; -C only your own |
port -a -t TYPE -p tcp PORT |
Allow a service type to use another port |
port -l |
List which ports belong to which type |
boolean -l |
Booleans with state and description |
permissive -a DOMAIN |
Put a single domain into permissive mode |
-d |
Delete an own rule again |
semanage fcontext only changes the rules. The files get their new label when you run restorecon.
Examples
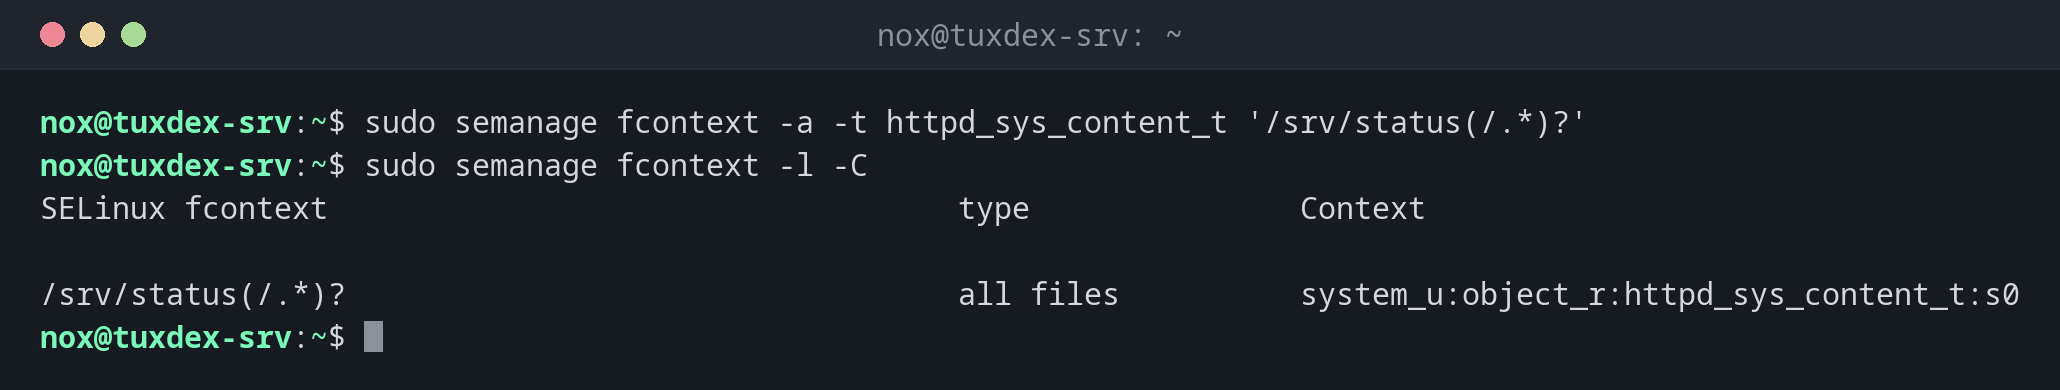
Let nginx serve a new directory:
sudo semanage fcontext -a -t httpd_sys_content_t '/srv/status(/.*)?'
sudo semanage fcontext -l -C
SELinux fcontext                                   type               Context

/srv/status(/.*)?                                  all files          system_u:object_r:httpd_sys_content_t:s0
Then apply the rule to the existing files with sudo restorecon -Rv /srv/status.
Show the ports the web server may use:
sudo semanage port -l | grep -E '^http_port_t'
http_port_t                    tcp      80, 81, 443, 488, 8008, 8009, 8443, 9000
http_port_t                    udp      80, 443
Allow an additional port:
sudo semanage port -a -t http_port_t -p tcp 8090
sudo semanage port -l -C
SELinux Port Type              Proto    Port Number

http_port_t                    tcp      8090
The port already belongs to another type:
sudo semanage port -a -t http_port_t -p tcp 8081
Port tcp/8081 already defined, modifying instead
Port 8081 is defined as transproxy_port_t; semanage reassigns it instead of adding it.
When do I need it?
- When a service serves files from an unusual directory, such as
/srv/status - When a service should listen on a port that isn't its default
- To see which own SELinux changes were made on a server (
-l -C)
Look at the existing rules first
semanage fcontext -l | grep /var/www shows how the default directories are labeled.
Copy the type from there for your own directory.
chcon doesn't last
chcon -t httpd_sys_content_t FILE changes a label directly, but the next relabel or
restorecon resets it. For lasting changes, always use semanage fcontext.
Distribution differences
| Debian | Ubuntu | RHEL | Arch | |
|---|---|---|---|---|
| SELinux | not active (AppArmor instead) | not active (AppArmor instead) | active, enforcing |
not active |
| Package | policycoreutils-python-utils (only if SELinux is set up) |
policycoreutils-python-utils (only if SELinux is set up) |
sudo dnf install policycoreutils-python-utils |
not in the official repositories |
Related commands
restorecon · setsebool · audit2allow · ls